
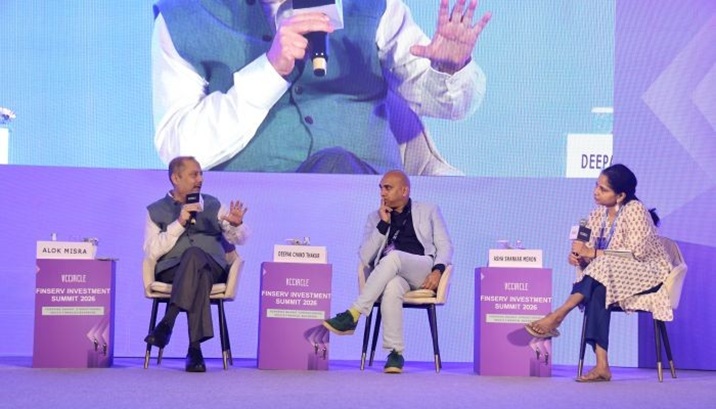
New Delhi, Sept. 22 -- Compliance has become central to financial businesses not just because the regulators are tracking it more closely but also because the markets are rewarding good governance, said panellists at the VCCircle Finserv Investment Summit 2026.
"There are [two] companies with similar financial performance, both listed. One is trading at 0.6x book value, the other is trading at 3x BV. This is the premium [markets are placing] on governance," said Alok Misra, CEO and director of Microfinance Industry Network (MFIN).
"From recent events, you can see how the Reserve Bank of India (RBI) is forcing people to go public, the big ones at least. Once you get listed, the market is also watching you. So there is dual scrutiny with smart people, analysts also tracking, analysing every bit of information [along with the regulatory scrutiny]," he said.
Misra said regulations have also become more broadbased. While regulations earlier focused on board composition and board practices, they have gone beyond into information technology, cyber-resilience, client protection, and adherence to the Digital Personal Data Protection Act, he said.
Deepak Chand Thakur, co-founder and CEO of banking and digital payment software solutions provider Network People Services Technologies Ltd, said that the inflexion point for this seems to have been around the pandemic years after when digital adoption was widespread.
"With COVID, the whole world changed and digital (technologies) played a very important role in this... [with that, compliance tasks] came as a compulsion, not an option. Your payments now have a digital layer, your banking has a digital layer, your move to a completely virtual [environment]," he said.
Challenges, solutions
This shift has come with its challenges.
"Compliance has never been easy, but the easier part of this transition has been on the governance side with regard to board composition, board evaluation... risk dashboards," said Misra.
"The complicated part has been the [managing] of the integrity of your IT systems and the threat of cyber attacks and, second, the AI factor. As institutions start using AI in their compliance and GRC [governance, risk, compliance] frameworks, there are consequences. Many are not capable of handling it but everyone wants to experiment with it," he said.
These are challenging also because of the fast pace at which these are changing, and the difficulty small and medium players have in quickly responding to these threats.
The regulations, when trying to keep up, can sometimes place "utopian" demands on these entities, said Misra.
Thakur said that regulations and criteria to be met should be made completely clear to everyone. "If there is any ambiguity, the execution of the same policy can differ from one organisation to the next. An example of a clear-cut actionable directive is mandating FRM [Fraud Risk Management] framework, instead of broadly saying you need to tackle fraud, which has such a wide canvas."
Misra said what regulators could do is implement directives in phases, with the most important first, then the second most important and so on.
Thakur also pointed out that compliance in India is still tackled in fragments and that it needs to be tackled with a unified GRC platform. "It has to move faster towards a tool-driven, unified approach and away from the [fragmented] consultative approach," he said.
Published by HT Digital Content Services with permission from VC Circle.