
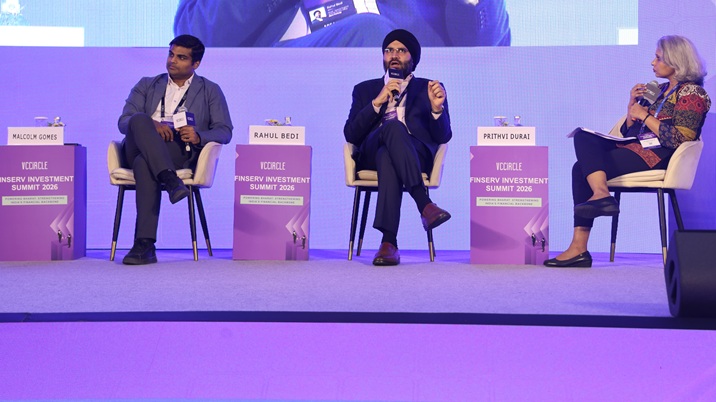
New Delhi, Sept. 22 -- Banks, fintech companies and other organisations can no longer treat customer information as private property but instead must operate as strict data custodians as they face a major overhaul of their data operations ahead of the enforcement of the Digital Personal Data Protection (DPDP) Act, panellists at the VCCircle Finserv Investment Summit 2026 said.
The panellists included Malcolm Gomes, Chief Operating Officer at IDfy, and Rahul Bedi, who heads special projects and the MD and CEO's office at Hero FinCorp. At a panel discussion titled 'Consent Economy: How DPDP Will Reshape Banking, Fintech and Financial Innovation', held in Mumbai on Friday, they detailed the operational, technological, and cultural shifts financial institutions must make as India transitions toward a consent-driven economy with the enactment of the DPDP Act.
"What used to happen earlier was one single checkbox, and you (companies) pretty much owned the data. Now, the shift will be that organisations will no longer be the owners of that data; they will become custodians of that data. So, the power will now be handed back to the consumer to decide what gets used where, for how long, till when companies can store it, and what uses it actually contributes," Bedi said.
The DPDP Act is India's data privacy law designed to regulate the processing of digital personal data while safeguarding individual privacy rights. The government has mandated full substantive enforcement, requiring organisations to fully comply with consent rules, data security safeguards, breach notifications, and penalty mechanisms by May 13, 2027.
"You need to have a certain global standing to attract certain kinds of investments. If India wants to be the R&D hub of the world, having this kind of scaffolding is imperative," said Gomes.
Referring to data as the new oil, Bedi said organisations would be able to acknowledge their entire data estate, which was earlier getting siloed across separate units-such as customer service, loan origination systems, loan management systems, and central data repositories.
"We're looking at this as an enterprise-wide transformation journey because we will be able to look at data holistically. Second, we will be able to reach out to our consumers, rebuild that entire trust we have with them, and third, come out with products and services catered to different use cases," Bedi said.
Gomes outlined three essential pillars every organisation must address for the law's on-the-ground implementation. One, managing consent transparently while balancing user experience. Two, "purging out" unnecessary, duplicated, outdated, or redundant data across backup databases and legacy forms. Three, re-evaluating personal data shared with vendors and third-party processors-such as card printers or marketing agencies-to establish verifiable proof, such as purge receipts post-processing, to confirm data is deleted once a task is completed.
Bedi said that consent must function as a seamless two-way street. "You give consent, but you also have to give them a mechanism to withdraw consent," he said, arguing that withdrawing consent should be as simple, channel-agnostic, and user-friendly as granting it.
Terming the exercise a herculean task for Hero FinCorp, Bedi advised prioritising high-ticket transactions first. "Start from the most data-rich set of customers you have. Look at what all you have, and then start working backwards."
Emphasising how the enactment requires a cultural mindset shift within organisations, Gomes said the number of parties involved would straddle different teams. "Legal has to be involved, tech has to be involved, security has to be involved, procurement has to be involved," he said. "This has to be driven from the top. It has to be top of mind, which a CEO has to make."
Published by HT Digital Content Services with permission from VC Circle.